Twosense Blog
BLOG LISTINGS
July 23, 2025
In hospitals, clinicians are under constant pressure—not just from patient loads or administrative tasks, but from the...
July 16, 2025
In Healthcare, Identity Is a Clinical Problem—Not Just a Security One In hospital environments, authentication is...
June 25, 2025
Passwordless authentication has become the gold standard in security for many organizations. Biometric scans,...
June 18, 2025
When we talk about contact center compliance, most people picture a list of frameworks and checkboxes: PCI, SOC 2,...
June 13, 2025
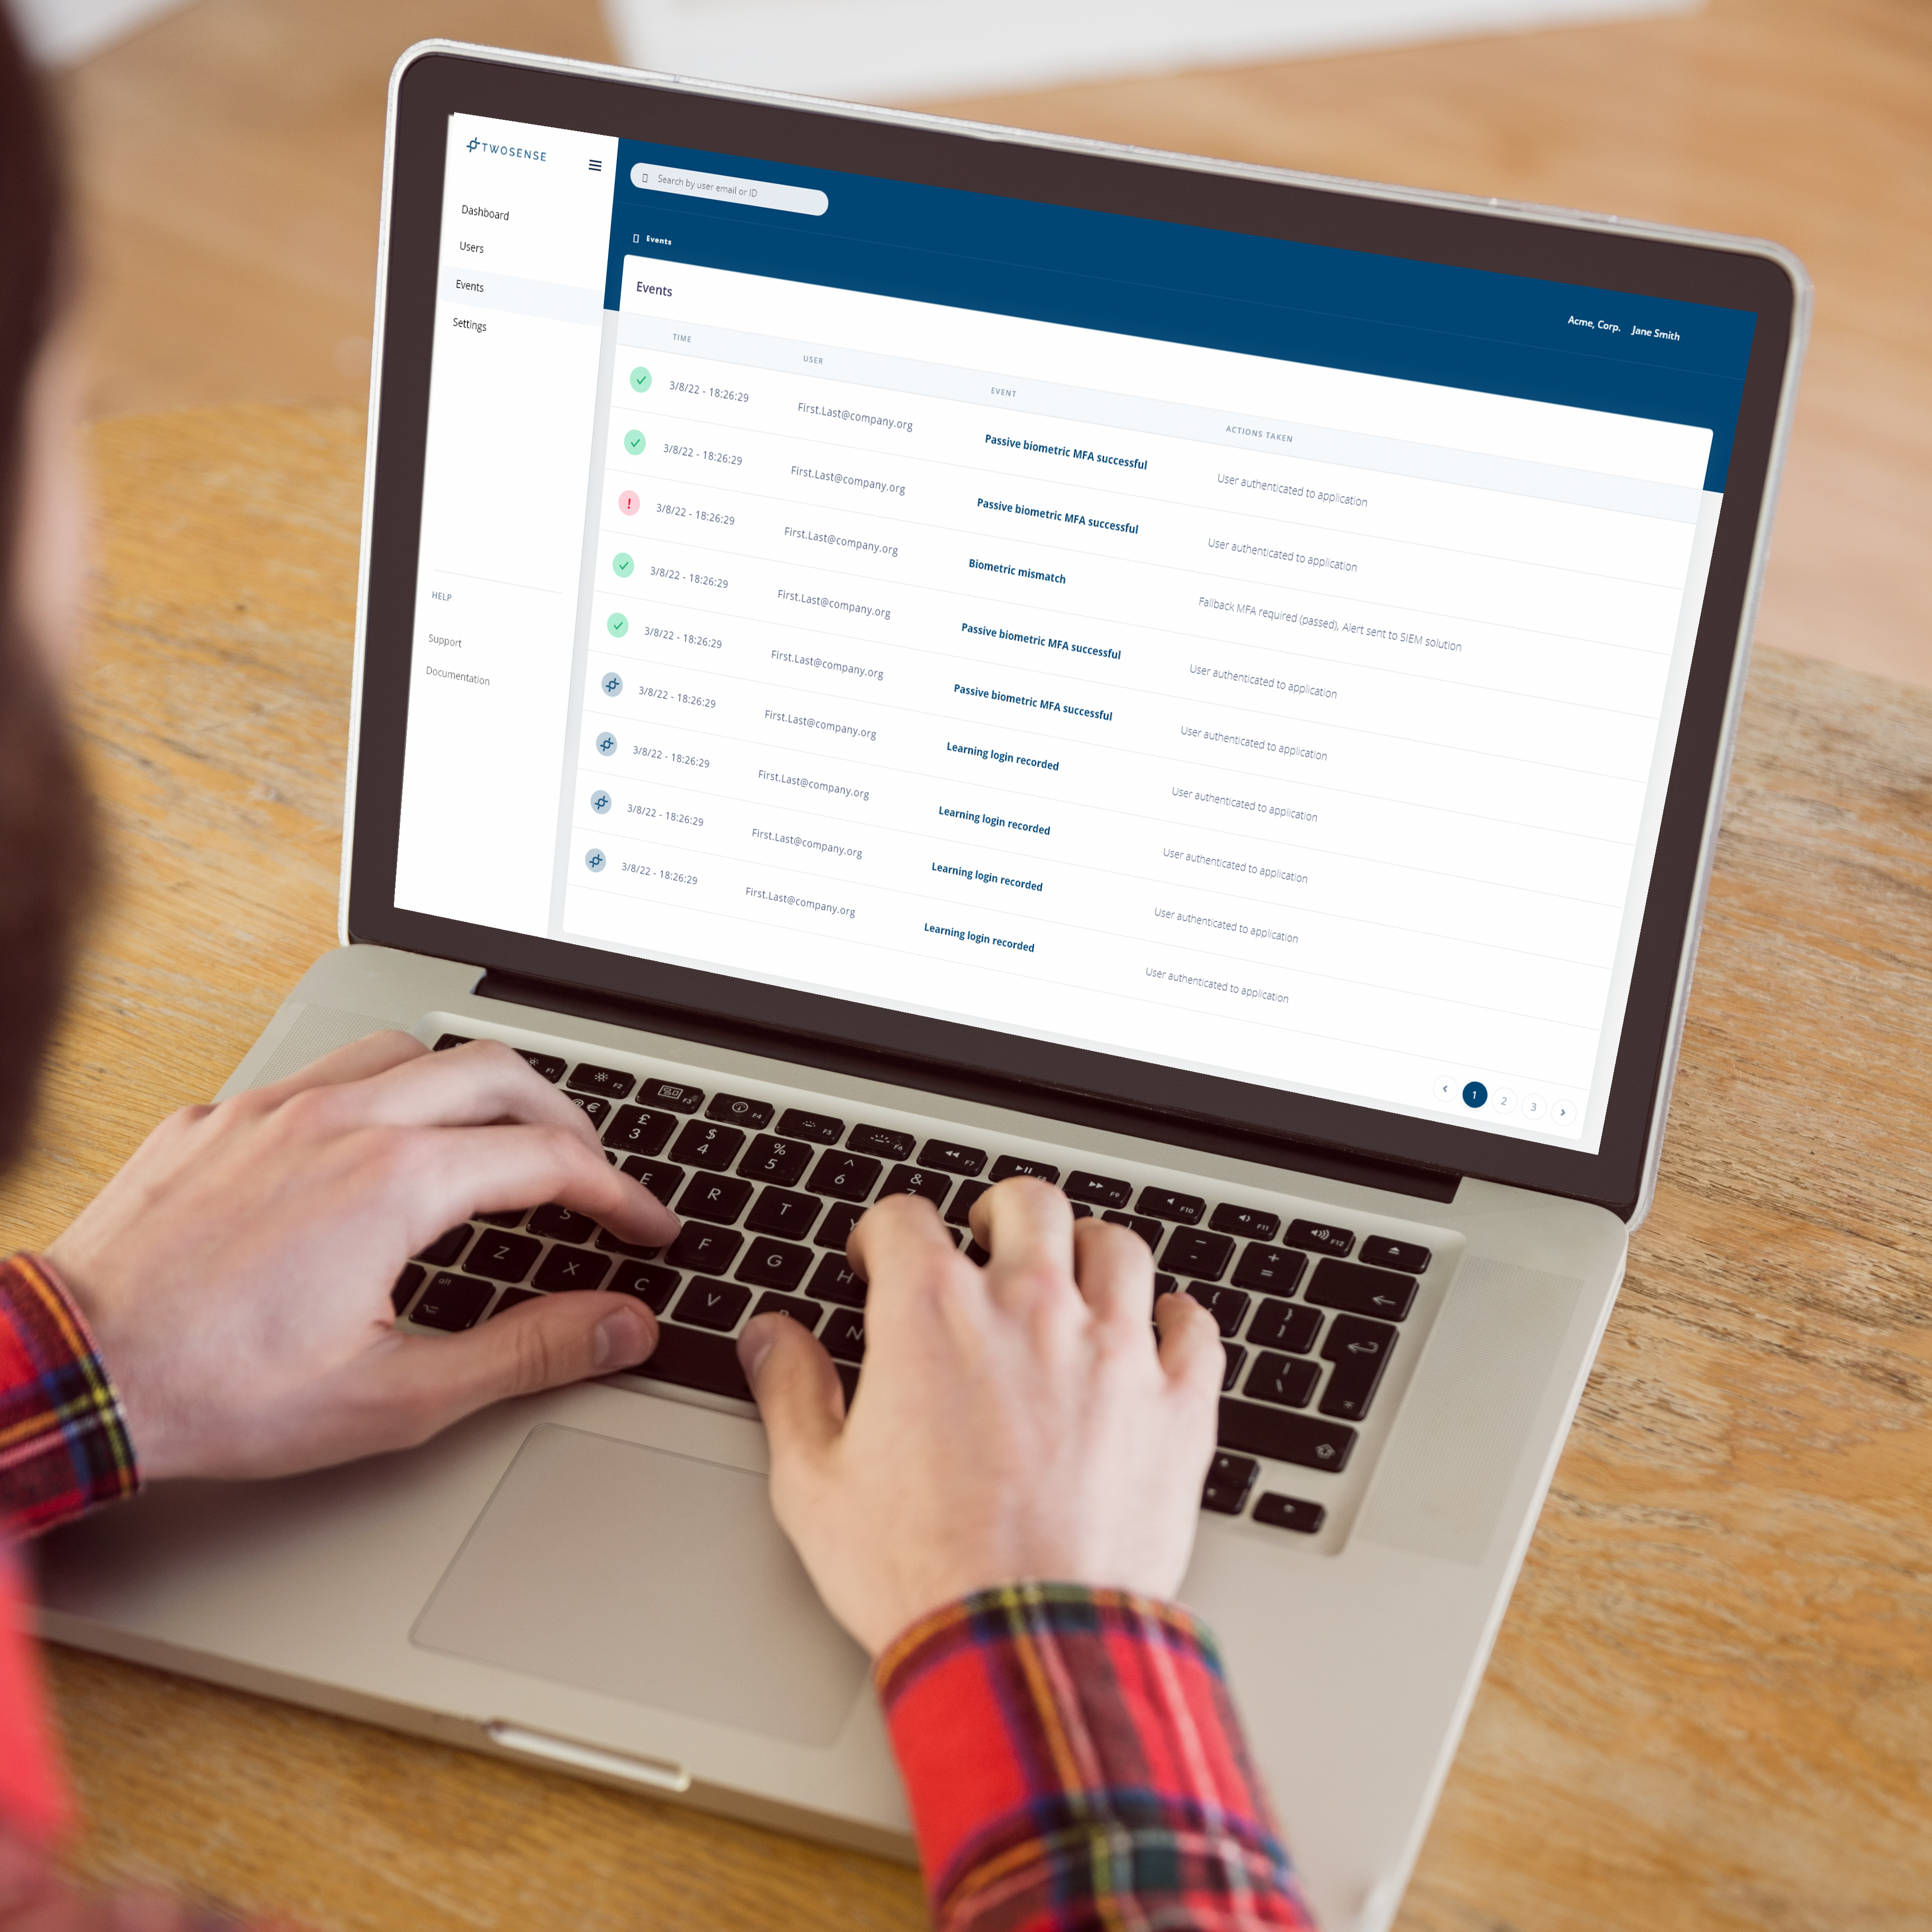
Identity and access management in the contact center has reached a turning point. For years, IT and security teams have...
June 4, 2025
Contact centers invest heavily in securing their infrastructure, preventing cyberattacks, and maintaining compliance....
Posts by Tag
- 2FA (8)
- Agent Identity (4)
- Agile (1)
- Authenticator Abuse (1)
- Automated MFA (6)
- Banks (1)
- Behavioral Authentication (4)
- Behavioral MFA (27)
- Biometrics (20)
- BPO (22)
- Burnout (1)
- CAEP (2)
- CCaaS (1)
- Clean Desk MFA (1)
- Compensating Controls (2)
- Compliance (18)
- Contact Centers (59)
- Continuous Access Evaluation (12)
- Continuous Authentication (109)
- Continuous Identity (10)
- Continuous Identity Verification (1)
- Continuous MFA (27)
- Cryptocurrency (1)
- Culture (2)
- Cyber Insurance (1)
- Cybersecurity (27)
- Data Breach (12)
- Data Science (1)
- Deep Work (1)
- Epic (1)
- FAQ (8)
- Flow State (1)
- Fraud Prevention (1)
- Hard Token Alternative (1)
- Hard Tokens (1)
- Health Systems (12)
- Healthcare (4)
- HIPAA (2)
- Hospitals (10)
- IAM (1)
- Identity Access Management (4)
- Identity Security (1)
- Infosec (14)
- Machine Learning (5)
- Mental Health (3)
- MFA (5)
- MFA Fatigue (1)
- Multi-Factor Authentication (51)
- Pass-Through Authentication (1)
- Passive Biometrics (11)
- Passive MFA (1)
- Password Sharing (2)
- Passwordless (12)
- PCI Compliance (18)
- PCI DSS (14)
- Phishing (5)
- Phishing-Resistant MFA (12)
- Preparedness (1)
- Press Release (1)
- Prompt Bombing (3)
- RFPs (1)
- Session Hijacking (1)
- Session Security (1)
- Shared Workstations (7)
- SOC2 (1)
- Social Engineering (4)
- Software MFA (1)
- Twosense Team (1)
- Unauthorized Users (2)
- Unphishable MFA (11)
- WAHA (1)
- Webinar (1)
- WFH (4)
- Zero Trust (10)
Recent Posts
Sign Up for our Blog
We will never share your email address with third parties.