BLOG LISTINGS
November 16, 2026
The AI You Approved Can Still Go Wrong When people hear "rogue AI," they tend to picture something out of a movie: a...
November 11, 2026
What Happened at Bayview When a health system announces a data breach, most people picture an outside attacker breaking...
November 4, 2026
AI Is Already Logging In as People AI assistants and agents now log in, type, and click on people's behalf, and the...
October 22, 2026
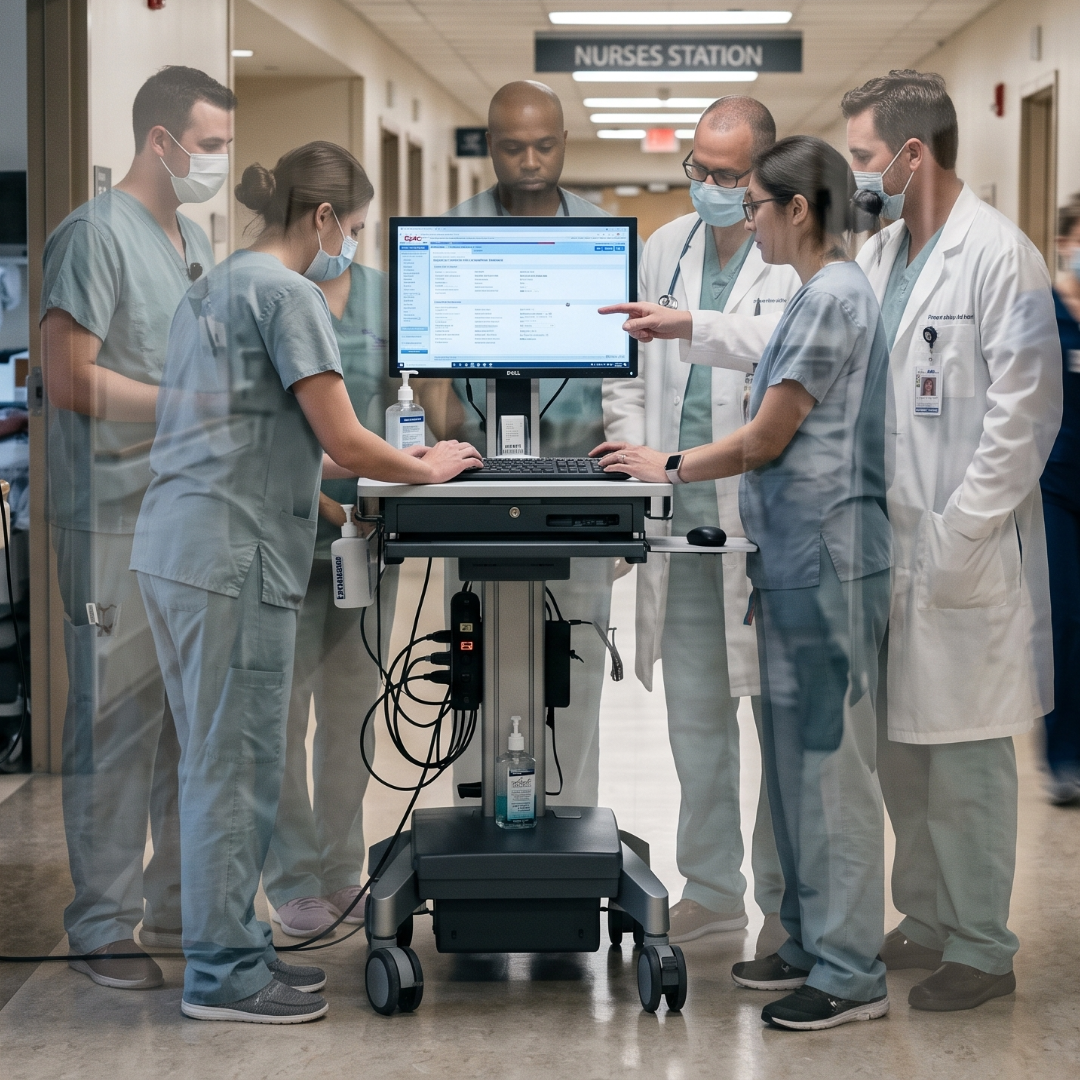
Why Timeouts Exist Session timeouts exist because organizations need some way to close the gap between a login and...
October 20, 2026
The Tradeoff Everyone Assumes Security and productivity get treated as opposite ends of the same lever in most health...
October 15, 2026
A Frustration With a Number Attached Every conversation about authentication friction in health systems tends to start...