Twosense Blog
BLOG LISTINGS
October 8, 2026
Two Terms, Two Different Jobs The two terms sound similar enough that they get used interchangeably in conversations...
October 6, 2026
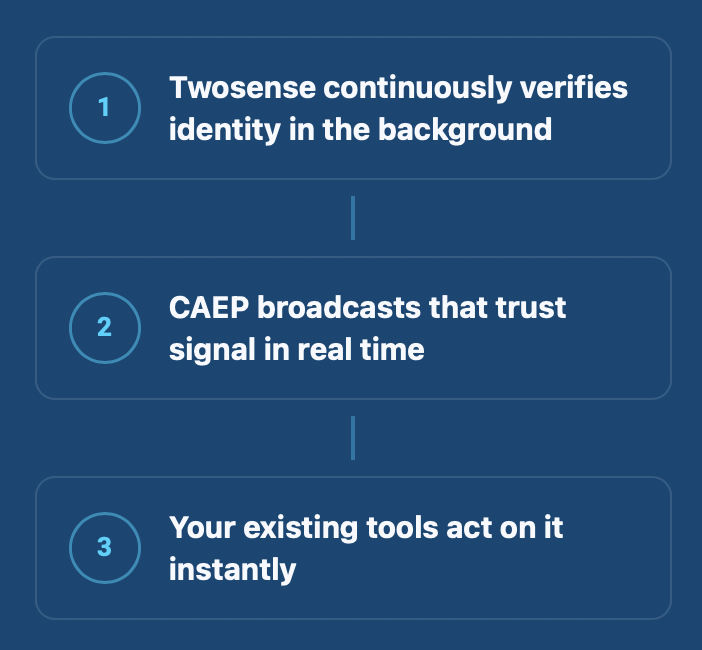
Not a New Way to Authenticate The Continuous Access Evaluation Profile, or CAEP, has started showing up in identity and...
October 1, 2026
A Fair Amount of Skepticism Is Warranted Health Systems security teams have earned the right to be skeptical of...
September 30, 2026
Our team hears some version of the same story from almost every health system it talks to: a passwordless pilot goes...
September 29, 2026
What Zero Trust Got Right Zero Trust changed how security teams think about access. Instead of assuming that anything...
September 25, 2026
Yes. Continuous Authentication verifies identity once a second, every second a session is active, using passive...
Posts by Tag
- 2FA (8)
- Agent Identity (4)
- Agile (1)
- Authenticator Abuse (1)
- Automated MFA (6)
- Banks (1)
- Behavioral Authentication (4)
- Behavioral MFA (27)
- Biometrics (20)
- BPO (22)
- Burnout (1)
- CAEP (3)
- CCaaS (1)
- Clean Desk MFA (1)
- Compensating Controls (2)
- Compliance (18)
- Contact Centers (59)
- Continuous Access Evaluation (12)
- Continuous Authentication (110)
- Continuous Identity (11)
- Continuous Identity Verification (1)
- Continuous MFA (27)
- Cryptocurrency (1)
- Culture (2)
- Cyber Insurance (1)
- Cybersecurity (27)
- Data Breach (12)
- Data Science (1)
- Deep Work (1)
- Epic (1)
- FAQ (8)
- Flow State (1)
- Fraud Prevention (1)
- Hard Token Alternative (1)
- Hard Tokens (1)
- Health Systems (13)
- Healthcare (4)
- HIPAA (2)
- Hospitals (10)
- IAM (1)
- Identity Access Management (4)
- Identity Security (1)
- Infosec (14)
- Machine Learning (5)
- Mental Health (3)
- MFA (5)
- MFA Fatigue (1)
- Multi-Factor Authentication (51)
- Pass-Through Authentication (1)
- Passive Biometrics (11)
- Passive MFA (1)
- Password Sharing (2)
- Passwordless (12)
- PCI Compliance (18)
- PCI DSS (14)
- Phishing (5)
- Phishing-Resistant MFA (12)
- Preparedness (1)
- Press Release (1)
- Prompt Bombing (3)
- RFPs (1)
- Session Hijacking (1)
- Session Security (1)
- Shared Workstations (7)
- SOC2 (1)
- Social Engineering (4)
- Software MFA (1)
- Twosense Team (1)
- Unauthorized Users (2)
- Unphishable MFA (11)
- WAHA (1)
- Webinar (1)
- WFH (4)
- Zero Trust (10)
Recent Posts
Sign Up for our Blog
We will never share your email address with third parties.